HIPAA and security
How we handle your patients' data
These safeguards are in place before any work with protected health information starts.
A Business Associate Agreement first
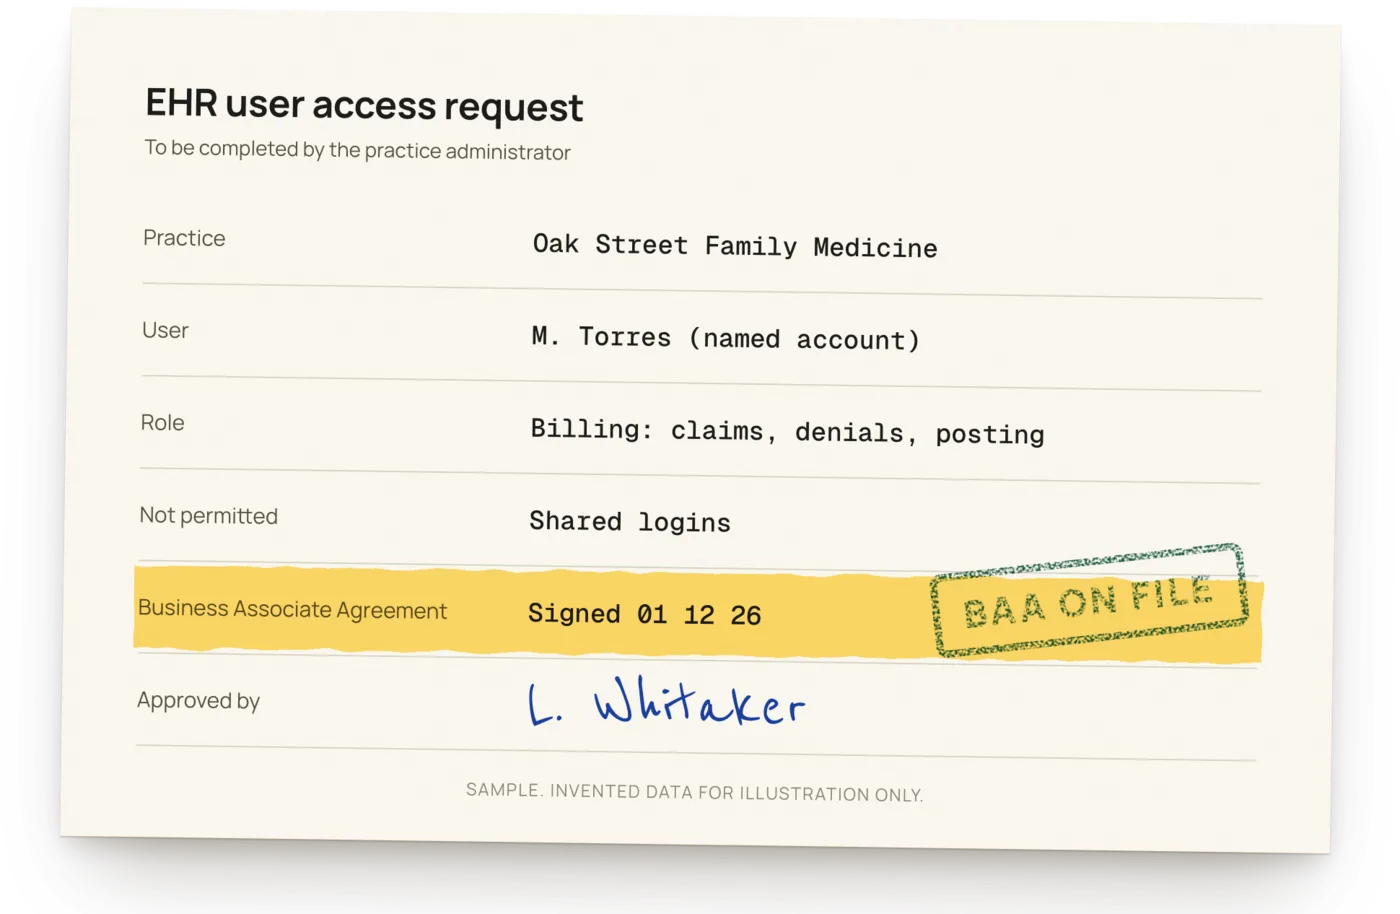
We sign a BAA with you before we access any protected health information.
Only the data we need
We ask for what a task requires. Audits start with summary reports wherever possible.
Role based access
People get access based on their role, through named accounts instead of shared logins.
Audit logs
Access and activity in our systems are logged, so anything can be looked back on.
A secure way to share data
Patient data shouldn't come through website forms. We'll agree on a secure method with you before any of it is shared.
Vendors
Any vendor that handles protected health information has to meet our contract and security requirements, including a BAA where one is required.
Where the work happens
Your billing work is done in the United States. Some payer and client contracts restrict offshore access to patient data, so if yours do, send them over and we can go through them together.
Keep patient data out of our forms
The forms on this website are for general inquiries. Please don't include patient names, dates of birth, member IDs or anything else about a patient.
Find out what your claims are leaving behind
Send us your denial and A/R reports and you'll have a written report within 48 hours, for free. You can keep your current biller while you decide.